JWT Decoder
Paste a JSON Web Token to decode its header and payload, inspect claims, and check expiration. Runs fully in your browser - decode-only, no secret required.
Paste a JWT to decode its header and payload.
Encoded TokenValid JWT
Runs entirely in your browser. Your token never leaves the page. Avoid pasting production tokens into any online decoder.
Decoded Header
{
  "alg": "HS256",
  "typ": "JWT"
}
Decoded PayloadActive
{
  "sub": "1234567890",
  "name": "John Doe",
  "iat": 1516239022,
  "exp": 4070908800
}- Issued at
- 2018-01-18T01:30:22.000Z (9 years ago)
- Expires at
- 2099-01-01T00:00:00.000Z (in 72 years)
Decoded SignatureHS256
SflKxwRJSMeKKF2QT4fwpMeJf36POk6yJV_adQssw5c
Verifying the signature requires the issuer's secret or public key, which this tool does not handle.
How to Use the JWT Decoder
Inspect any JSON Web Token in your browser. The decoder splits the token, base64url-decodes the header and payload, and surfaces expiration metadata.
How to Use
- Paste your JWT into the input area
- The header and payload are decoded automatically as you type
- Review the status badge for Active, Expired, or Not yet valid tokens
- Use the copy buttons to grab the decoded JSON
- Click "Load sample" to see what a decoded token looks like
What is a JWT?
- JSON Web Token: A compact, URL-safe token format defined by RFC 7519, made of three base64url-encoded segments separated by dots
- Header: Describes the signing algorithm (alg) and token type (typ)
- Payload: Carries the claims - data such as subject (sub), issued at (iat), and expiration (exp)
- Signature: Computed from the header and payload using a secret or private key, used for integrity checks
Security Notice
Decoding a JWT is not the same as verifying it. Read this carefully before using the tool.
- Decoding does not verify: This tool only base64url-decodes the segments. It does not check the signature against a key, so it cannot tell if the token was tampered with
- JWTs are not encrypted: The payload of a standard JWT is plain JSON encoded with base64url - anyone who has the token can read its contents
- Do not paste production tokens: Treat real tokens like passwords. Avoid pasting access tokens for live systems into any online tool
- Client-side only: Your token is processed entirely in your browser and is never sent to a server
Common Use Cases
- API Debugging: Inspect access and refresh tokens returned by your auth provider
- Expiration Checks: Quickly see whether a token has expired or is not yet valid
- Claim Inspection: Read user identifiers, roles, scopes, and custom claims
- Learning: Explore the structure of JWTs while studying authentication flows
Built by me
View all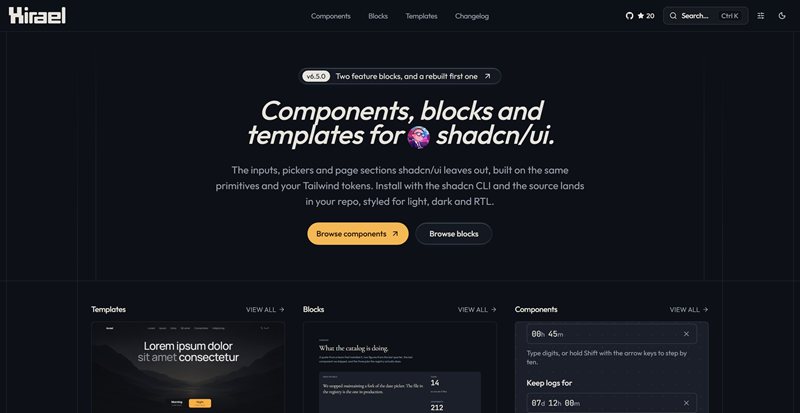
Hirael
Components, blocks and templates for shadcn/ui. The inputs, pickers and page sections shadcn leaves out, built on the same primitives and installed with the shadcn CLI so the source lands in your repo.
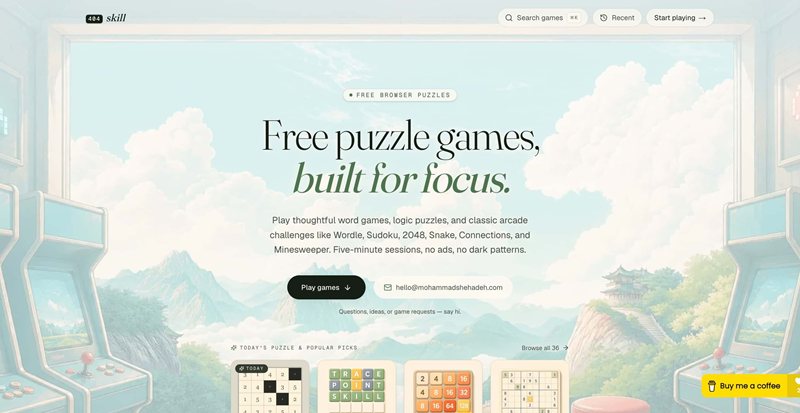
404 Skill
A quiet arcade for word games, logic puzzles, and classic browser games. Play focused sessions without ads or tracking.
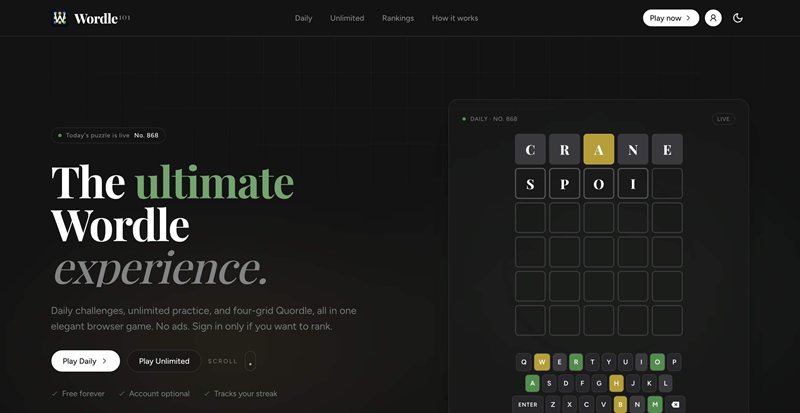
Wordle 101
A Wordle-inspired word guessing game with daily puzzles and streak tracking.